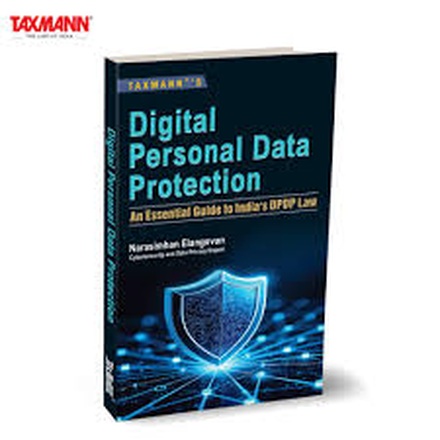
Taxmann's Digital Personal Data Protection - An Essential Guide to India's DPDP Law - Edition 2026
| Author : | Narasimhan Elangovan |
|---|
| Taxmann's Digital Personal Data Protection — An Essential Guide to India's DPDP Law by Narasimhan Elangovan, cybersecurity and data privacy expert (2026 Edition), is a practical read-through guide to the Digital Personal Data Protection Act, 2023 together with the DPDP Rules, 2025. It covers the scope of digital personal data and extra-territorial application, Data Principals, Data Fiduciaries, Data Processors, Significant Data Fiduciaries and Consent Managers, the requirements of valid consent and the legitimate uses permitted without it, the obligations of a Data Fiduciary including reasonable security safeguards, breach notification, erasure and the Data Protection Officer, children's data and verifiable parental consent, the rights and duties of Data Principals, cross-border transfer, exemptions, the Data Protection Board of India and appeals to the TDSAT, and the Schedule of penalties. Paperback. ISBN 9789375618614. |


Tags: Cyber Law, Information Technology Law, Data Protection Rights, Digital Data Protection
Taxmann's Digital Personal Data Protection — An Essential Guide to India's DPDP Law by Narasimhan Elangovan, cybersecurity and data privacy expert, published by Taxmann, is a practical introduction to India's data protection regime. This is the 2026 Edition. Paperback. ISBN 9789375618614.
The Digital Personal Data Protection Act, 2023 sat largely dormant until the DPDP Rules, 2025 were notified, which set the regime running on a phased commencement with the substantive obligations falling due over the following months. That has turned data protection from a policy topic into a compliance deadline for almost every Indian organisation that holds customer, employee or user data — and for most of them, the first requirement is simply to understand what the law asks of them. This guide is written for that reader.
Key Features
- 2026 Edition, published by Taxmann
- An essential guide rather than a section-by-section commentary — written to be read through
- Authored by a cybersecurity and data privacy practitioner, not only from the legal side
- Covers the DPDP Act, 2023 together with the DPDP Rules, 2025
- Practical orientation towards building a compliance programme
- Paperback · English
Coverage
Scope and Key Concepts. What counts as digital personal data; the application of the Act to processing within India and to processing outside India connected with offering goods or services in India; and the exclusions.
The Actors. The Data Principal, the Data Fiduciary, the Data Processor, the Significant Data Fiduciary and the additional obligations attaching to that class, and the Consent Manager and its registration.
Grounds for Processing. Consent — the requirements of free, specific, informed, unconditional and unambiguous consent, the notice that must accompany it, and withdrawal; and the legitimate uses for which personal data may be processed without consent.
Obligations of a Data Fiduciary. Accuracy and completeness; reasonable security safeguards; personal data breach notification to the Board and to affected Data Principals; erasure on withdrawal of consent or when the purpose is served; the publication of contact details of the Data Protection Officer; and the grievance redressal mechanism.
Children's Data. Verifiable parental consent, the prohibition on tracking, behavioural monitoring and targeted advertising directed at children, and the exemptions available to certain classes of fiduciary.
Rights and Duties of Data Principals. The right to access information about processing, the right to correction and erasure, the right to grievance redressal, the right to nominate — and the duties imposed on Data Principals themselves.
Cross-Border Transfer. Transfer of personal data outside India and the restrictions the Central Government may impose.
Exemptions. Processing for enforcement of legal rights, judicial and regulatory functions, prevention and investigation of offences, corporate restructuring, and the exemptions available to the State and to startups.
The Data Protection Board of India. Composition and appointment, the complaint procedure, the powers of the Board, digital-by-design functioning, and appeal to the Telecom Disputes Settlement and Appellate Tribunal.
Penalties. The Schedule of financial penalties, the factors relevant to determining quantum, and the consequences of failing to prevent a personal data breach.
The DPDP Rules, 2025. The notice format, consent manager obligations, the standards for reasonable security safeguards, breach intimation timelines, the periods for retention and erasure, verifiable consent for children, and the phased commencement schedule.
Who Should Buy This Book?
- Data Protection Officers and privacy leads
- Chief Information Security Officers and IT security teams
- Compliance officers and internal auditors
- In-house counsel and Company Secretaries
- Chartered Accountants advising on regulatory compliance
- Technology lawyers and privacy consultants
- Founders and product managers building consent and data flows
- HR heads processing employee data
- Students of cyber law and information technology law
- Corporate and institutional libraries
Why Choose This Book?
The DPDP Act is short, and the temptation is to read it and assume the work is done. In practice the difficulty is not the text but the translation — what a compliant notice actually looks like, what record of consent will stand up, which of your vendors is a processor and what your contract with them must say, how quickly a breach must be reported and to whom. A guide is a better instrument for those questions than a commentary, because they are answered in sequence rather than by section.
The author being a cybersecurity and data privacy practitioner matters for the same reason. Much of DPDP compliance is engineering and process rather than drafting — consent capture, retention schedules, access controls, breach detection — and a book written from that side is more useful to the team that has to implement it than one written purely from the statute.